


On this page
How to pick the clause for each policy
- 1Write one policy per command. Supabase's RLS guide does, and says a for all policy "hides which operation each rule was meant to cover".
- 2select and delete: using only. The expression filters the rows the command sees, and rows that fail it are skipped with no error.
- 3insert: with check only. The expression is checked against the row being added, and the insert fails if it is false or null.
- 4update: both. using picks which existing rows can be changed; with check is evaluated against "the proposed new contents of the row, not the original contents". Leave with check out and the using expression is applied to the new row as well.
- 5update also needs select. Supabase says an update without a matching select policy "will not work as expected", and Postgres applies the select policies whenever an update reads columns, for example in its where clause.
- 6To see which clause a live policy has, read pg_policies: qual is the using expression and with_check the with check expression. A null with_check on an update or all policy means using is doing both jobs.
SQL select policyname, cmd, qual, with_check from pg_policies where schemaname = 'public' and tablename = 'todos';
One example for each command
Each example is for a todos table whose user_id column holds the owner's id, as in Supabase's RLS guide.
SELECT: using filters what you can read
A row whose using expression is false or null is not returned. No error, just fewer rows.
See the fix
create policy "Users can view their own todos"
on public.todos for select
to authenticated
using ( (select auth.uid()) = user_id );
INSERT: with check validates the new row
The check runs against the row being inserted. If the app sends someone else's user_id, or none, the insert fails with new row violates row-level security policy.
See the fix
create policy "Users can create their own todos"
on public.todos for insert
to authenticated
with check ( (select auth.uid()) = user_id );
UPDATE: using finds the row, with check validates the result
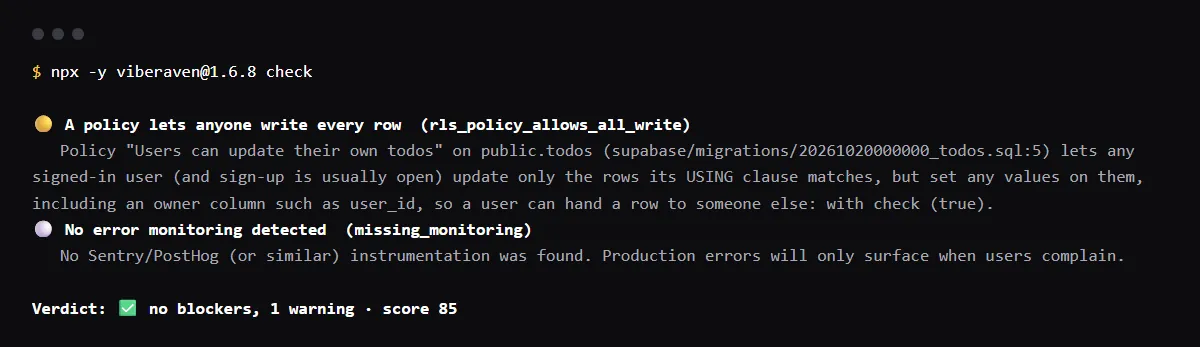
using limits the update to the user's own rows; with check stops them from setting user_id to someone else. A row that fails using is skipped, and a result that fails with check stops the statement.
See the fix
create policy "Users can update their own todos"
on public.todos for update
to authenticated
using ( (select auth.uid()) = user_id )
with check ( (select auth.uid()) = user_id );
DELETE: using decides what can be removed
Rows that fail using are not deleted and nothing is reported, so check the affected row count when a delete seems to do nothing.
See the fix
create policy "Users can delete their own todos"
on public.todos for delete
to authenticated
using ( (select auth.uid()) = user_id );
ALL: one policy for every command
A for all policy applies to select, insert, update and delete. With only a using expression, Postgres uses it for new rows too. It works, but separate policies show what each command is allowed to do.
See the fix
create policy "Users manage their own todos"
on public.todos for all
to authenticated
using ( (select auth.uid()) = user_id )
with check ( (select auth.uid()) = user_id );
When either clause is just true
with check (true) on insert lets any signed-in user create rows that belong to anyone, and using (true) on update or delete lets them change or remove every row. The Security Advisor flags always-true conditions, and the using (true) guide below covers when they are fine.
Related guides
Official docs behind this checklist
Browse all launch guides · Read resources · How to make and check your next change
FAQ for builders before launch
Which clause is behind new row violates row-level security policy?
With check, or the lack of any policy that allows the row. The message means a row being inserted or updated did not pass a with check expression (or the using expression an update reuses as one) for the role the request ran as. The RLS policy error guide linked below walks through the full diagnosis after a deploy.
Can a SELECT policy have WITH CHECK?
No. Postgres says "A SELECT policy cannot have a WITH CHECK expression", and a delete policy cannot have one either. The reverse holds for insert: "An INSERT policy cannot have a USING expression".
What happens if an update policy has no WITH CHECK?
Postgres uses the using expression for both jobs: which rows can be updated and which new rows are allowed. That is fine when using checks ownership, and lets any values through when it is true.