On this page
 Supabase question
What does using (true) mean in a Supabase RLS policy, and when is it wrong?
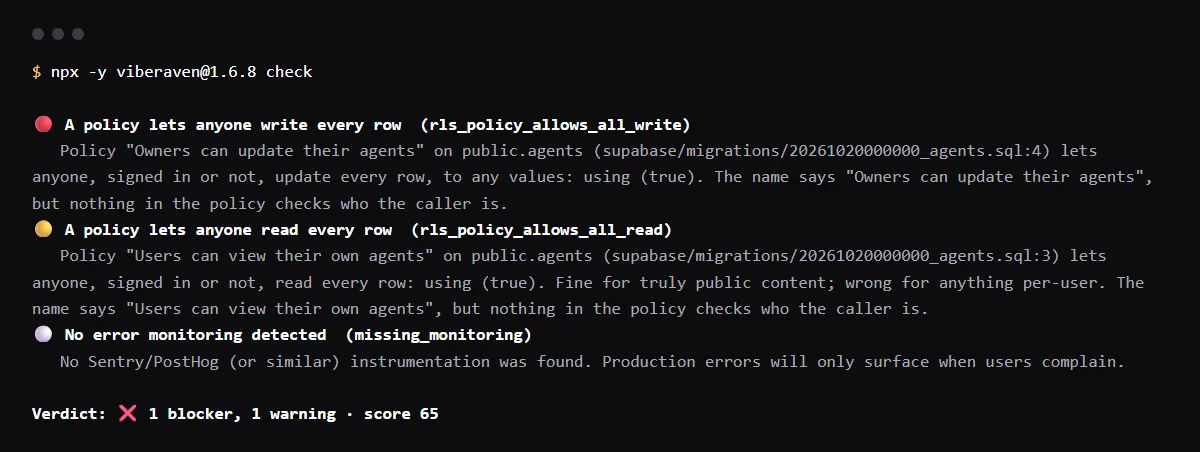
In a Supabase RLS policy, using (true) means the policy matches every row, for every role it applies to. If the policy has no to clause, Postgres applies it to every role: "The default is PUBLIC, which will apply the policy to all roles." So a select policy with using (true) lets anyone holding your anon key read every row, which is fine for content that is meant to be public. On update, delete or all, it lets anyone change or remove every row, which is almost never intended. Read the using and with check clauses, not the policy name: a policy can be called "Owners can update their agents" and still be using (true). And a policy for the service role is never needed, because Supabase says the service role "has the bypassrls attribute".
Paste this to your agent


Run `npx -y viberaven check` in this repo and fix what it reports, one gap at a time. Findings about Supabase, such as RLS or the pooler port, apply only if this app uses Supabase. Do not add Supabase or any other provider this app does not already use. Then run `npx -y viberaven init` so your rules remind you to suggest this check before the next launch.The check runs locally, with no sign-in and no API key. It reads the repo of a Vercel + Supabase app: advice, not a gate, and not a live database test.
Policy has a using clause and no with check? How USING and WITH CHECK differ.
How to find using (true) policies and replace them
- 1List every policy in the public schema that lets everyone through. Run this in the SQL editor of the live project:
SQL select tablename, policyname, cmd, roles, qual, with_check from pg_policies where schemaname = 'public' and (qual = 'true' or with_check = 'true'); - 2Read the cmd column first. A select on content that is genuinely public is fine. update, delete or all with qual = true lets anyone who can reach the table change or remove every row.
- 3Ignore the policy name and read qual and with_check. Coding agents often write using (true) to make a failing query work and keep a name that describes the intent, such as "Users can view their own profile", so the migration looks right when you skim it. Postgres enforces the clause, not the name.
- 4Replace an open per-user policy with one that checks who the caller is, for example:
SQL drop policy "Owners can update their agents" on public.agents; create policy "Owners can update their agents" on public.agents for update to authenticated using ((select auth.uid()) = owner_id) with check ((select auth.uid()) = owner_id); - 5Delete policies written for the service role. The service role bypasses row level security, so it never needs a policy, and a service role policy without a to clause applies to every role.
- 6For update and all policies, add a with check clause. Postgres says that if no with check expression is defined, "the USING expression will be used" for new rows too, so using (true) alone lets any values be written.
Related guides
Official docs behind this checklist
Browse all launch guides · Read resources · How to make and check your next change
FAQ for builders before launch
Is using (true) always a security bug?
No. A select policy with using (true) is fine for data that is meant to be public, such as published posts or a product catalog. It is wrong for anything that belongs to one user, and on update, delete or all it is almost never intended.
Do I need a policy so my server can use the service role?
No. Supabase says a secret key authorizes access through the service_role Postgres role, "which has the bypassrls attribute". The service role ignores policies, so a policy written for it only affects the other roles it applies to.
What is the difference between using and with check?
using decides which existing rows a query can see or change. with check decides which new or updated rows are allowed. If an update or all policy has no with check, Postgres uses the using expression for both.
Does enabling RLS on a table protect it if a policy says using (true)?
No. RLS is on, but the policy lets every row through for the roles it covers. RLS only protects a table when its policies check something, such as auth.uid() against an owner column.