On this page
 Supabase publishable and secret keys
Supabase API keys: publishable, secret, anon or service role?
Short answer
Two of the four Supabase API keys are public and two are not. The publishable key (sb_publishable_) and the legacy anon key (eyJ) belong in browser code: a request with either one runs as anon or authenticated, so table grants and row level security decide what it reaches. The secret key (sb_secret_) and the legacy service_role key (eyJ) run as service_role, which bypasses row level security, so they stay on the server. The new pair replaces the legacy pair, which Supabase is deprecating by the end of 2026.
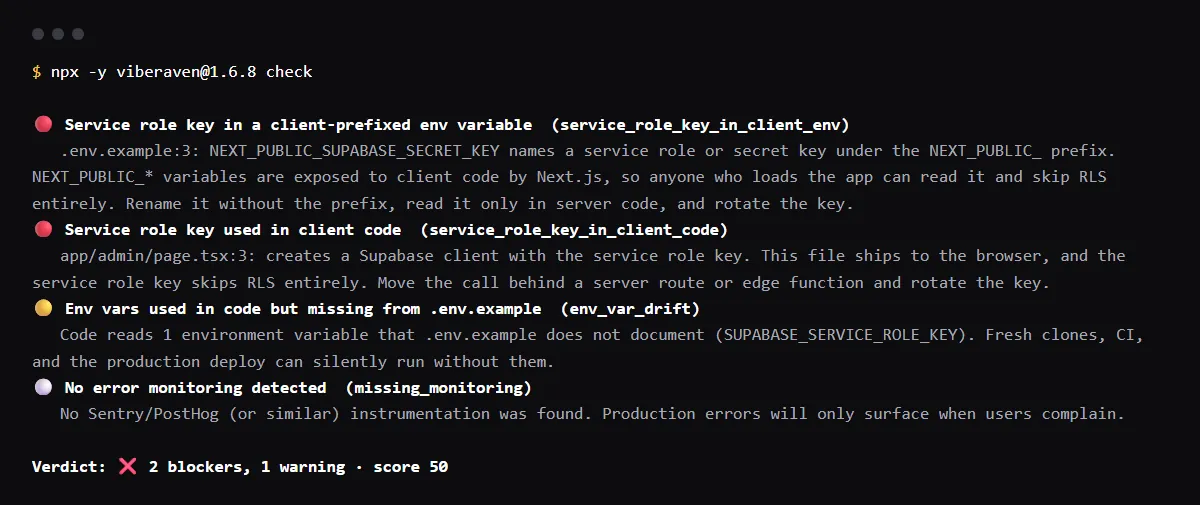
npx -y viberaven@1.10.0 checkOn a fixture repo on 2026-11-03 it printed "src/lib/supabase.ts:4: contains a hardcoded sb_secret_ key" as service_role_key_in_client_code and gave no finding for the sb_publishable_ key on the line above. It also reports a service role or secret key under a NEXT_PUBLIC_ or VITE_ name as service_role_key_in_client_env.
Or ask your coding agent to "run npx -y viberaven@1.10.0 check and fix what it reports".
Use this from your agent
- Claude Code: 7 read-only tools; public repos only.
claude mcp add --transport http viberaven https://viberaven.dev/mcp - Codex: same server, from the Codex CLI.
codex mcp add viberaven --url https://viberaven.dev/mcp - In your repo: writes Vercel + Supabase check rules for your agent (what it writes).
npx -y viberaven init
Paste this to your agent


Run `npx -y viberaven@1.10.0 check` in this repo and fix privileged Supabase keys in client code or public-prefixed variables. Keep publishable keys public with appropriate RLS; do not print key values. Report live checks you could not run.Open your app's repo in your coding agent, then paste this request.
Seeing the publishable or anon key in your bundle is expected. Before launch, check what that public key can reach.
Quick answer
The anon key becomes the publishable key, and the service_role key becomes the secret key. Both pairs work at the same time until you deactivate the legacy keys in Settings > API Keys, which Supabase says you can reverse.
Timeline, checked 2026-10-25: Supabase's API keys guide says the legacy keys are deprecated by the end of 2026, and the announcement on GitHub plans to delete them and remove them from the docs and dashboard in late 2026, date to be confirmed.
Is the anon key the same as the publishable key?
Not the same key, but the same job. Supabase's migration guide says the publishable key "carries the same low privileges as the anon key, so your Row Level Security policies behave the same". Only the format differs: the anon key is a long-lived JWT, the publishable key starts with sb_publishable_ and is not a JWT. Creating one "doesn't revoke your legacy keys".
What is the Supabase publishable key?
The public key that replaces the anon key. Supabase calls it "Safe to expose online": a web page, a mobile or desktop app, a CLI, your source code. It "only reaches what Row Level Security allows", so it goes where the anon key was, in the frontend.
What is the Supabase secret key?
The key that replaces service_role. Supabase says "Policies never apply to a secret key", but table grants still do: a missing grant returns a permission error, even for service_role. Keep it in server environment variables without a NEXT_PUBLIC_ or VITE_ prefix, and use it only in route handlers, server actions, Edge Functions and jobs you run.
To copy one from the dashboard, see Where do I find the Supabase service role key?
What is the difference between publishable, secret, anon and service_role keys?
Two pairs that do the same two jobs: a public key for the browser and a server key that skips RLS. Supabase's API keys docs list anon as the "Legacy version of publishable keys" and say Supabase is "deprecating the anon and service_role keys by the end of 2026". Since both pairs map to the same roles, a table without RLS is exactly as open with either public key. Move one client at a time, then deactivate the legacy pair.
Looking for the anon or publishable key itself? See What is the Supabase anon key, and where do I find it?
The key is copied, but the app still fails. What next?
Separate client setup from data access. A missing URL or key can fail before any request is sent. An invalid-key response needs the project URL and key checked together. A successful request with no rows is a different problem: inspect the signed-in user, grants, policies and query filters. Do not replace a public key with a privileged key to silence an error.
For a Vite app, first check the matching env variable and client code. If the request reaches your tables, follow the two-user access checks.
A 401 that says Invalid API key means the project does not accept the key it got, such as a key from another project: the Invalid API key fix.
How to check your keys and move to publishable and secret keys
- 1Find every place a privileged key could be. Search the repo, env files included, for service role and secret key names and for a raw sb_secret_ value:
Terminal grep -rnE "service_role|SERVICE_ROLE|sb_secret_|SECRET_KEY" . --exclude-dir=node_modules --exclude-dir=.git - 2In a Vercel + Supabase app, npx -y viberaven@1.10.0 check does part of that search from the project root: it reports a service role or secret key under NEXT_PUBLIC_ or VITE_ as service_role_key_in_client_env, and a browser file that creates a Supabase client with that key as service_role_key_in_client_code. It does not flag other secrets, so keep the search above:
Terminal npx -y viberaven@1.10.0 check - 3Any service role or secret key behind NEXT_PUBLIC_, or read in a file that starts with "use client", is in the browser bundle. Rename the variable without the prefix, read it only in server code (a route handler, a server action, an Edge Function), and treat the old key as leaked.
- 4Check that every table in the public schema has row level security on, because that is what protects your data from anyone holding the anon or publishable key. Run this in the SQL editor of the live project; every row it returns is a table without row level security:
SQL select schemaname, tablename from pg_tables where schemaname = 'public' and rowsecurity = false; - 5Create the new keys in the dashboard under Settings, API Keys. Put the publishable key (sb_publishable_) where the anon key was, in the frontend. Put the secret key (sb_secret_) only where the service_role key was used on the server, in environment variables without a public prefix.
- 6If a service role or secret key was ever in client code, a NEXT_PUBLIC_ variable or a public repository, rotate it. Supabase's API keys docs give the order for a secret key: create a new one, replace the old one everywhere, confirm every component uses the new one, then delete the compromised key, which cannot be undone. A legacy key is deactivated instead, which can be reversed.
Which key is which, and what a wrong env name looks like
The first table sets the four keys side by side. The second records what supabase-js did locally with a missing or misnamed env value, before any request reached Supabase.
The four keys side by side
Both pairs resolve to the same Postgres roles, so the switch changes the key format, not what a key may do. It does change what GitHub notices after a leak. In our read of 512 public Lovable repos, 29 committed a service role or secret key, and 25 of them held only the legacy service_role key, which is not on GitHub's list of supported secret scanning patterns. A server moved to sb_secret_ is on that list.
| Key | Starts with | Runs as | In browser code? | On GitHub's secret scanning list? |
|---|---|---|---|---|
| publishable | sb_publishable_, not a JWT | anon, or authenticated with a signed-in user's token; RLS applies | Yes | No, and it is public anyway |
| anon (legacy) | eyJ, a JWT | anon, or authenticated with a signed-in user's token; RLS applies | Yes | No, and it is public anyway |
| secret | sb_secret_ | service_role, which bypasses RLS; table grants still apply | No. A browser gets 401 Unauthorized, a script that sets its own headers does not | Yes, and push protection covers it |
| service_role (legacy) | eyJ, a JWT | service_role, which bypasses RLS | No | No |
Same client code, three env configurations
On 21 October 2026 we built a small Vite client-config module, then passed its exported URL and key to supabase-js. These are local constructor results, not hosted API requests. The values were disposable placeholders, not credentials.
A client that initializes can still fail its next request. Inspect that request before changing a public key or weakening an RLS policy.
| Configuration | Observed result | Next check |
|---|---|---|
| Neither expected variable is set | supabaseUrl is required. | Set the project URL under the name the code reads. |
| URL is set; env has ANON_KEY while code reads PUBLISHABLE_KEY | supabaseKey is required. | Match the env name and the client read. |
| URL and expected public-key variable are both set | Client initialized locally | Run the app action and inspect the actual response; initialization is not a data-access test. |
Reviewing key usage with your coding agent
For an existing Vercel + Supabase repo, the existing VibeRaven Skill can help check for privileged keys referenced in client code. Fix a missing env value or variable-name mismatch directly first. Use the repository pass when the task includes reviewing key exposure or migration access; do not substitute a secret key to make a browser request succeed.
Read the linked Skill and use the parts relevant to your task. From your app folder, with Node.js 20 or newer, run the command below. No global Skill installation is required for this one-off check. It writes findings under .viberaven/. Exit code 1 means blockers were found, not necessarily that the command failed; inspect the output.
Read .viberaven/agent-tasklist.md and .viberaven/gate-result.json. Check each finding against the actual code, make the smallest authorized fix, then rerun the same command and your project checks. Report the changed files, remaining findings and checks you could not perform. Keep keys and private data out of chat.
This is a repository check, not a live database test. It cannot confirm deployed grants, rotate a key or verify hosted environment values. A clear result is not proof that the app is secure. Test the affected app behavior separately; provider changes and deployment follow your normal approval process.
npx -y viberaven@1.10.0 checkNeed to fix this in your existing app?
If the diagnosis points to a variable-name mismatch, ask for that one client-setup change. Then rebuild and repeat the failing action. Do not paste real keys into the request.
Sign in to the VibeRaven website with Google and connect the app folder on your computer, with Node.js 20 or newer. Keep the connection terminal open. Claude Code, Codex or Gemini CLI must be installed and signed in. The agent uses your own provider account, and usage may be billed there.
The website sends the code change to your agent on your computer. Repository checks are advice, not a gate, and not a live database test. Review the diff, project checks and running app before keeping it. This does not read your hosted keys, change provider settings or deploy for you.
Related guides
Official docs behind this checklist
Browse all launch guides · Read resources · How to make and check your next change
FAQ for builders before launch
Is the service role key the same as the secret key?
Same access, different key. Both authorize requests as the service_role role and bypass row level security. Secret keys are the replacement: you can create one per backend component and delete a leaked one without touching the others, and Supabase returns HTTP 401 when a browser sends one.
Does switching to the new keys protect data that is already exposed?
No. The publishable key has the same job as the anon key, so a table without row level security is as open with one as with the other. Turn on row level security and add policies first; the key switch does not do it for you.
Can I keep using the anon and service_role keys for now?
Until Supabase retires them. Its API keys docs say it is "deprecating the anon and service_role keys by the end of 2026", with no exact day given as of 2026-10-25, so switching before the deadline is the safer plan.