On this page
 Supabase change
Supabase "permission denied for table" (42501) on new tables since October 30, 2026: the Data API grants change
Short answer
"permission denied for table" (42501) on a new Supabase table since October 30, 2026 means the table was created after Supabase began applying its Data API change to existing projects, so it no longer gets automatic grants for anon and authenticated, and supabase-js, REST and GraphQL calls to it fail until a migration grants it. Add grant select on table public.your_table to authenticated; (and each other role and command the app uses) to the migration that creates the table, after its row level security and policies; tables from before the change keep their grants, so if the error names an older table, the cause is something else, such as a policy that reads an ungranted table.
npx -y viberaven@1.8.0 checkWith auto_expose_new_tables = false under [api] in supabase/config.toml, it reports each table with row level security that your client code queries and no migration grants as data_api_grant_missing, with the grant line to add.
Or ask your coding agent to "run npx -y viberaven@1.8.0 check and fix what it reports".
Use this from your agent
- Claude Code: 7 read-only tools; public repos only.
claude mcp add --transport http viberaven https://viberaven.dev/mcp - Codex: same server, from the Codex CLI.
codex mcp add viberaven --url https://viberaven.dev/mcp - In your repo: writes Vercel + Supabase check rules for your agent (what it writes).
npx -y viberaven init
Paste this to your agent


Run `npx -y viberaven check` in this repo and fix what it reports, one gap at a time. Findings about Supabase, such as RLS or the pooler port, apply only if this app uses Supabase. Do not add Supabase or any other provider this app does not already use. Also check that new tables in my migrations have the grants they need. Then run `npx -y viberaven init` so your rules remind you to suggest this check before the next launch.The check runs locally, with no sign-in and no API key. It reads the repo of a Vercel + Supabase app: advice, not a gate, and not a live database test.
Already seeing the error on an older table? What permission denied for table means, and the grant that fixes it.
Check this in your repo
Find the new tables in your repo that no migration grants
Add auto_expose_new_tables = false under [api] in supabase/config.toml, as in the local test step below, then run the command below from your app folder with Node.js 20 or newer. It lists each public table that has row level security and a policy, that your client code queries through supabase-js, and that no migration grants, as data_api_grant_missing, with the grant line to add. A table a migration grants to anon or authenticated while row level security is off comes out as data_api_grant_without_rls, with or without the config line.
It is a repository check, not a live database test: it does not read the grants your hosted project holds, tables made in the dashboard, or tables only a policy or your server reads.
npx -y viberaven@1.8.0 checkWhat it printed on a fixture repo
Historical CLI 1.7.2 capture. The current command above uses 1.7.8; its output can differ.
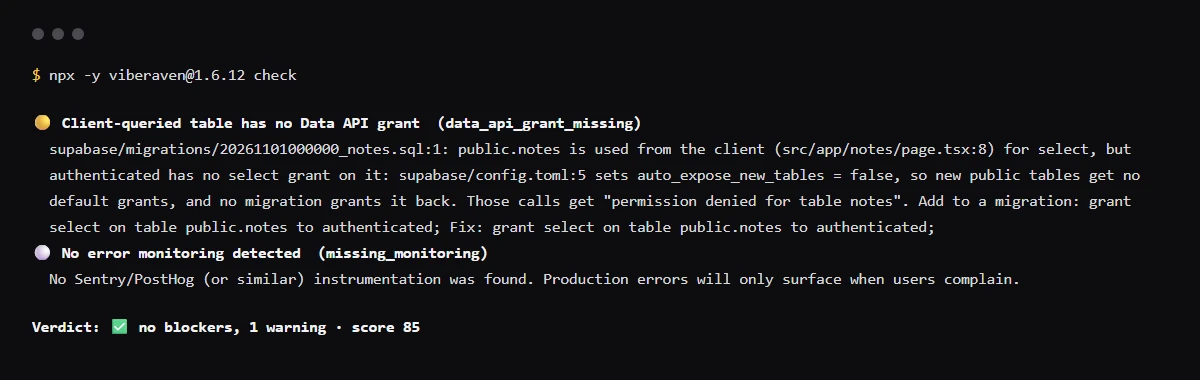
On 2026-10-23 we ran it on a small Next.js fixture repo made for this page, not a customer repo. Its supabase/config.toml sets auto_expose_new_tables = false under [api], one migration creates public.notes with row level security and an owner-only select policy but no grant, and a client component reads it with supabase.from('notes').select('id, body').limit(50). The output is below, with the temp folder shortened to ~/notes-app. A warning is not a blocker, so the exit code was 0.
After a second migration added that grant line, the same command reported no data_api_grant_missing finding. With the config line removed and no grant, it reported none either, because it looks for missing grants only when the repo turns default grants off.
$ npx -y viberaven@1.7.2 check

viberaven check · ~/notes-app

🟡 Client-queried table has no Data API grant  (data_api_grant_missing)
   supabase/migrations/20261101000000_notes.sql:1: public.notes is used from the client (src/app/notes/page.tsx:8) for select, but authenticated has no select grant on it: supabase/config.toml:5 sets auto_expose_new_tables = false, so new public tables get no default grants, and no migration grants it back. Those calls get "permission denied for table notes". Add to a migration: grant select on table public.notes to authenticated; Fix: grant select on table public.notes to authenticated;
⚪ No error monitoring detected  (missing_monitoring)
   No Sentry/PostHog (or similar) instrumentation was found. Production errors will only surface when users complain.

Verdict: ✅ no blockers, 1 warning · score 85
Fix: viberaven fix · Details: ~/notes-app/.viberaven/agent-tasklist.md
Why this matters
Before the change, a table created in the public schema was granted to anon, authenticated and service_role the moment it existed, so a table an agent made was reachable through the API right away, with or without row level security. Supabase's announcement moved that to an explicit grant: the default for new projects from May 30, 2026, rolled out gradually, and for all existing projects from October 30, 2026. A Supabase CLI pull request merged in August says the earlier default change for new projects "never landed", so check your project's Data API settings rather than assume the change has reached it. Grants decide whether a role can reach a table at all; row level security decides which rows it sees, and Supabase says that part does not change. Only the Data API is affected, which is what supabase-js, REST and GraphQL calls use; an app that talks to Postgres over a direct connection string is not. In an AI-built app the break shows up in two places: the first table a prompt adds after the switch, and old migrations replayed into a new project or a fresh local database that has the new default. Both look like an app that worked yesterday and now cannot read its own data.
What to check now that the change is live
- 1Leave the tables you have alone. Supabase staff confirmed in the announcement thread that existing tables on existing projects keep their current grants and are not revoked by the October 30 rollout.
- 2See which roles can reach a table today, with the query from Supabase's 42501 troubleshooting page:
SQL select grantee, privilege_type from information_schema.role_table_grants where table_name = 'your_table'; - 3See whether new tables in public still get the automatic grants on your project today, with the query from Supabase's Securing your API page. A tables row for anon or authenticated means a table the postgres role creates in public is still granted to that role. The revoke in Supabase's announcement removes those rows.
SQL select case d.defaclobjtype when 'r' then 'tables' when 'S' then 'sequences' when 'f' then 'functions' end as object_type, a.grantee::regrole as role, string_agg(a.privilege_type, ', ' order by a.privilege_type) as privileges from pg_default_acl d cross join lateral aclexplode(d.defaclacl) a where d.defaclrole = 'postgres'::regrole and d.defaclnamespace = 'public'::regnamespace and a.grantee in ('anon'::regrole, 'authenticated'::regrole, 'service_role'::regrole) group by 1, 2 order by 1, 2; - 4In every migration that creates a table the app reaches, through supabase-js or through a policy, view or function that reads it as the caller, enable row level security, add policies and grant it, in that one migration. Supabase calls the three steps a unit, because Postgres rejects a query with no grant before any policy runs. Grant anon only on tables signed-out visitors read. If the table has a serial or identity column, Supabase staff suggest in the thread that you also grant usage on its sequence. On our local stack (Supabase CLI v2.119.0, auto_expose_new_tables = false) a signed-in insert into a serial table worked without that grant: the CLI's revoke, like the one in the announcement, takes usage and select on new sequences but leaves update, and Postgres accepts update for nextval. With every privilege on the sequences revoked, the serial insert failed with "permission denied for sequence items_serial_id_seq" and an identity insert still worked, as two other commenters in the thread say. No hosted project was tested, so grant usage on a serial column's sequence anyway. Adapted from Supabase's announcement, with row level security first and the anon policy and grant left as comments:
SQL alter table public.your_table enable row level security; create policy "users can read their own rows" on public.your_table for select to authenticated using (auth.uid() = user_id); grant select, insert, update, delete on public.your_table to authenticated; grant select, insert, update, delete on public.your_table to service_role; -- only if signed-out visitors read this table. The policy above is for -- authenticated only, so anon needs its own policy as well as the grant, -- here limited to rows marked public: -- create policy "visitors can read public rows" -- on public.your_table -- for select -- to anon -- using (is_public); -- grant select on public.your_table to anon; - 5Find the tables that still need that grant. With auto_expose_new_tables = false under [api] in supabase/config.toml, npx -y viberaven@1.8.0 check, run from the project root, reports each table with row level security that your client code queries and no migration grants as data_api_grant_missing, with the grant line to add. It reads the repo, so a table made in the dashboard needs the role query above:
Terminal npx -y viberaven@1.8.0 check - 6If a coding agent writes your migrations, put that rule in its instructions: every create table in public ships with row level security, policies and its grants in the same migration, including a table only a policy reads. Supabase's announcement suggests updating the agent's system prompt or using the Supabase agent skill, which includes the grants step.
- 7Read the 42501 message before you fix anything. "permission denied for table your_table" is a missing grant, and Supabase's hint names the GRANT to add. The table it names can differ from the one you queried: Postgres runs a policy with the privileges of the role making the query, so when a policy reads a table that role has no grant on, the error names that table. A blocked insert or update under row level security also returns 42501, with a different message, and clients often report both as a 401 or 403.
- 8Do not silence 42501 by granting a table that has RLS off. Supabase's docs say a table exposed through the Data API without RLS can be accessed by any role with matching grants, so a grant to anon gives every row to anyone with the key your frontend ships. Enable RLS and add policies first. Views count as tables here: Postgres default privileges for tables also cover views, so a new view needs its own grant. A view runs with its owner's rights unless it is created with (security_invoker = on), which is why Supabase's RLS guide says views bypass RLS by default. The same guide says a view over a protected table hands out every row its policies were meant to withhold. Create views with (security_invoker = on) before you grant them.
- 9Do not move the secret key into the browser to make the error go away. It bypasses every RLS policy, and it does not fix a missing grant: Supabase's API keys guide says a missing grant returns a permission error for service_role too. The guide lists a 401 for a secret key sent from a browser as a check the new keys add over the legacy service_role key, so do not count on that block for the old key.
- 10Treat the announcement's rollback as a last resort. Its bulk grant gives anon, authenticated and service_role select, insert, update and delete on all tables in schema public, including any without RLS. If you run it, list the tables without RLS first (the related guides below show a query and tools for that). The announcement itself says to revoke private tables one by one right after.
- 11If you build new projects from your migrations (one per client, staging, a fresh local database), add one migration after the last create table that grants each existing table the app reaches, through supabase-js or through a policy, view or function that reads it as the caller. Supabase staff confirmed in the thread that a reset with the new default leaves tables from older migrations without grants. Naming each table keeps private ones closed; a bulk grant opens them all.
- 12Search your migrations for default privilege statements. A grant there turns automatic grants back on for tables created after it, so a local reset can pass while a project with the new default fails. A commenter in the announcement thread says a baseline made with supabase db pull probably contains one:
Terminal grep -rni "alter default privileges" supabase/migrations - 13Test against the new behavior locally. With Supabase CLI v2.102.0 or later, add this to supabase/config.toml, run supabase db reset and use the app. Depending on your Supabase CLI version, leaving the key out can mean either behavior. A CLI pull request merged on 2026-06-10 made an unset key revoke the grants, in releases v2.106.0 through v2.115.0. The one merged on 2026-08-26 switched it back to auto-expose from v2.116.0, and on v2.119.0 our local stack with the key left out still granted new tables to anon and authenticated. So set it to false explicitly:
JSON [api] auto_expose_new_tables = false - 14Do not expect the change to close new functions. Postgres grants EXECUTE on every new function to PUBLIC, which includes every role, and its docs say a per-schema revoke cannot take a global default away. Supabase staff said in the thread that this is not handled on purpose. Revoke EXECUTE from public, anon and authenticated on each function only your server should call. Supabase's Securing your API page says new functions on existing projects also get EXECUTE for anon, authenticated and service_role, so a revoke from public and anon alone leaves any signed-in user able to call it.
- 15Do not read a quiet Security Advisor as proof that reads are scoped. Supabase's Advisors docs list using (true) on a read policy as a pattern lint 0024 detects, but the splinter source for that lint skips select policies with using (true) on purpose, because public reads are often deliberate. This page did not run the hosted Advisor, so we do not know which of the two your dashboard follows. Check a 42501 fix that adds a grant and a using (true) read policy yourself rather than waiting for the Advisor to flag it.
Related guides
Supabase and Postgres sources behind this page
- Supabase, Changelog: Tables not exposed to Data and GraphQL API automatically
- Supabase, Announcement thread and staff answers (discussion #45329)
- Supabase CLI, pull request #6337
- Supabase CLI, pull request #5524
- Supabase CLI, apps/cli-go/pkg/config/api.go on develop
- Supabase, Securing your API
- Supabase, Database API 42501 errors
- Supabase, Row Level Security
- Supabase, API keys
- Supabase, Advisors
- splinter, lint 0024 (always-true policies)
- Supabase CLI, db reset
- PostgreSQL, Privileges
- PostgreSQL, GRANT
- PostgreSQL, ALTER DEFAULT PRIVILEGES
- PostgreSQL, Row Security Policies
- PostgreSQL, CREATE VIEW
- PostgreSQL, Sequence Manipulation Functions
Browse all launch guides · Read resources · How to make and check your next change
FAQ for builders before launch
Do I need to do anything if I never add another table?
Not for the tables you have. Supabase staff confirmed that existing tables on existing projects keep their grants. You need explicit grants when you create a new table in public after the change reaches your project, or when you replay your migrations into a new project or a fresh local database that has the new default.
Does it affect apps that connect to Postgres directly?
No. Supabase says the change applies to the Data API, which supabase-js, REST and GraphQL use. An app that reads and writes over a direct connection string, through psql, an ORM or its own server, is not affected.
Will my RLS policies change?
No. Supabase says row level security behavior stays the same. A grant decides whether a role can reach a table at all; a policy decides which rows it sees. But Postgres runs a policy with the privileges of the role making the query, so any table a policy reads needs a select grant for that role too, or has to be read through a security definer function, which Supabase's RLS guide says to keep out of exposed schemas. A new lookup table such as team_members, read by a policy on an older table, breaks reads on the older table until it is granted.
Does it touch tables in storage, auth or my own schemas?
No. The announcement says tables in storage, auth, realtime and custom schemas keep their current grants and defaults.